
ISO/IEC 20000-1 is an international standard for Service Management Systems (SMS), commonly associated with IT Service Management (ITSM). It establishes requirements for organizations to plan, design, transition, deliver and improve services in a controlled and consistent way.
It can be used by organizations providing services to internal or external customers, including IT service providers, managed service providers, cloud and technology companies, shared-service organizations and other service businesses.
The standard focuses on establishing a systematic approach to service management rather than prescribing a particular technology, software platform or ITSM methodology. Its purpose is to help organizations demonstrate that their services are planned, delivered, monitored and improved through a defined management system.
Featured Snippet
ISO/IEC 20000-1 is used for what?
ISO/IEC 20000-1 is used to establish and maintain a Service Management System (SMS) that helps an organization consistently plan, design, transition, deliver and improve services while meeting agreed service requirements and delivering value to customers.
1. What Is ISO/IEC 20000-1?
ISO/IEC 20000-1 is the requirements standard within the ISO/IEC 20000 service-management family.
Its formal title is:
ISO/IEC 20000-1:2018 — Information technology — Service management — Part 1: Service management system requirements
It specifies requirements for an organization to establish, implement, maintain and continually improve an SMS.
Although the standard is strongly associated with IT service management, its underlying service-management principles can also be relevant to organizations providing other types of services.
ISO itself notes that the standard is increasingly being applied beyond traditional IT services to other service environments.
2. What Is a Service Management System?
A Service Management System (SMS) is the structured management framework an organization uses to control how its services are planned, delivered, monitored and improved.
Think of it as the management system behind the service.
For example, a SaaS company may provide:
Software Platform
But behind that platform are numerous service-management processes:
Customer onboarding
↓
Service availability
↓
Incident management
↓
Service requests
↓
Change management
↓
Release
↓
Service continuity
↓
Customer feedback
↓
Performance measurement
↓
Continual improvement
ISO/IEC 20000-1 provides the management-system framework for controlling these service activities.
3. ISO/IEC 20000-1 Is More Than an IT Help Desk Standard
This is one of the most important misconceptions.
Some organizations associate IT service management only with:
- Help desk
- Ticketing
- Incident management
- Technical support
Those are important, but ISO/IEC 20000-1 is much broader.
A mature SMS considers the complete service lifecycle.
Service Management
Planning
↓
Design
↓
Transition
↓
Delivery
↓
Monitoring
↓
Evaluation
↓
Improvement
ISO describes ISO/IEC 20000-1 as covering the planning, design, transition, delivery and improvement of services.
4. Why Does IT Service Management Matter?
Imagine a company where the IT department handles hundreds of incidents every month.
The organization may have:
- highly skilled engineers
- modern cloud infrastructure
- expensive monitoring tools
- cybersecurity products
- sophisticated applications
Yet customers still complain.
Why?
Because technology alone doesn’t guarantee effective service management.
The organization may lack:
- defined service levels
- clear ownership
- standardized processes
- escalation mechanisms
- change controls
- service continuity planning
- performance measurement
- customer feedback mechanisms
ISO/IEC 20000-1 addresses the management system around the service.
That distinction is important.
5. The Business Problem ISO/IEC 20000-1 Helps Address
Consider a typical IT service provider.
A customer reports:
“Our application is unavailable.”
Without a mature service-management system:
Customer → Help Desk → Engineer → Another Engineer → Vendor → Escalation → Customer waits
There may be confusion about:
- who owns the incident
- priority
- SLA
- escalation
- communication
- technical recovery
- customer notification
- post-incident review
With structured service management:
Incident
↓
Classification
↓
Priority
↓
Assignment
↓
Investigation
↓
Escalation if required
↓
Resolution
↓
Service Restoration
↓
Customer Communication
↓
Review / Improvement
The objective is not merely to close tickets.
The objective is to restore and manage services consistently.
6. Who Needs ISO/IEC 20000-1?
ISO/IEC 20000-1 can be relevant to many types of organizations.
ISO identifies its potential use by organizations demonstrating capability for the planning, design, transition, delivery and improvement of services, and by organizations monitoring and reviewing their SMS and services.
Potential users include:
1. IT Service Providers
Organizations providing managed IT services to customers.
Examples:
- Managed Service Providers
- IT outsourcing companies
- Infrastructure service providers
- Technical support providers
2. SaaS Companies
Software-as-a-Service organizations increasingly need structured approaches to:
- availability
- incidents
- changes
- releases
- service continuity
- customer support
ISO/IEC 20000-1 can provide a formal management-system framework around these activities.
3. Cloud Service Providers
Cloud environments depend heavily on controlled service operations.
Relevant areas can include:
- availability
- capacity
- continuity
- incident management
- change management
- supplier management
- service reporting
4. Data Centre and Infrastructure Providers
Organizations managing infrastructure services can benefit from structured service-management controls.
This can include:
- hosting
- infrastructure
- network services
- data-centre operations
- managed infrastructure
5. IT Support and Managed Service Companies
Organizations providing outsourced:
- Help Desk
- Desktop Support
- Network Support
- Application Support
- Infrastructure Support
can use ISO/IEC 20000-1 to demonstrate a structured service-management approach.
6. Internal IT Departments
ISO/IEC 20000-1 is not limited to companies selling IT services externally.
An internal IT department can also operate a Service Management System for the organization’s internal customers.
For example:
Corporate IT Department
serves:
- Finance
- HR
- Sales
- Operations
- Management
- Manufacturing
In this situation, employees become internal service users and the IT department operates as an internal service provider.
7. Global Capability Centres and Shared Services
Large organizations operating shared IT services across locations can use service management to establish greater consistency.
This can be particularly relevant where:
- multiple business units are supported
- services cross geographical boundaries
- third-party suppliers are involved
- service levels need to be measured
7. ISO/IEC 20000-1 and ITIL — Are They the Same?
No.
This is one of the most frequently asked questions.
ISO/IEC 20000-1
is an international standard containing requirements for a Service Management System.
ITIL
is a service-management framework and body of guidance/practices.
They are therefore not interchangeable.
ISO itself notes that organizations can incorporate approaches such as Agile, Lean, DevOps and ITIL into an ISO/IEC 20000-1-based service-management system.
A simplified view:
| ISO/IEC 20000-1 | ITIL |
|---|---|
| International standard | Service-management framework |
| Contains requirements | Provides practices/guidance |
| Supports conformity assessment/certification | Not itself an ISO certification standard |
| Management-system oriented | Practice-oriented |
| Can incorporate ITIL practices | Can support ISO/IEC 20000-1 implementation |
Practical example
An organization might use:
ISO/IEC 20000-1
for its formal Service Management System,
and
ITIL practices
to help design and improve specific service-management processes.
They can work together.
8. ISO/IEC 20000-1 vs ISO 9001
Another important question:
Is ISO/IEC 20000-1 just ISO 9001 for IT?
Again, no.
ISO 9001 is a general Quality Management System standard.
ISO/IEC 20000-1 is specifically focused on service management.
| ISO 9001 | ISO/IEC 20000-1 |
|---|---|
| Quality Management System | Service Management System |
| Broad industry application | Service-management focused |
| Customer and process quality | Service planning, delivery and improvement |
| Product/service conformity | Service requirements and service performance |
| General QMS framework | Service-management framework |
However, organizations can integrate the standards.
For example:
ISO 9001
ISO/IEC 20000-1
ISO/IEC 27001
can form a powerful integrated management framework for technology organizations.
9. ISO/IEC 20000-1 and ISO/IEC 27001
For IT organizations, another important relationship is with information security.
ISO/IEC 20000-1
asks:
How do we manage and deliver services effectively?
ISO/IEC 27001
asks:
How do we manage information-security risks?
A technology organization may need both.
Consider a cloud service provider.
It needs to manage:
Service
- Availability
- Incident
- Change
- Capacity
- Continuity
and:
Security
- Confidentiality
- Integrity
- Availability
- Access control
- Security risk
Integrating the two management systems can reduce duplicated processes and create stronger governance.
ISO’s own practical guide notes that ISO/IEC 20000-1 can be integrated with standards such as ISO 9001 and ISO/IEC 27001.
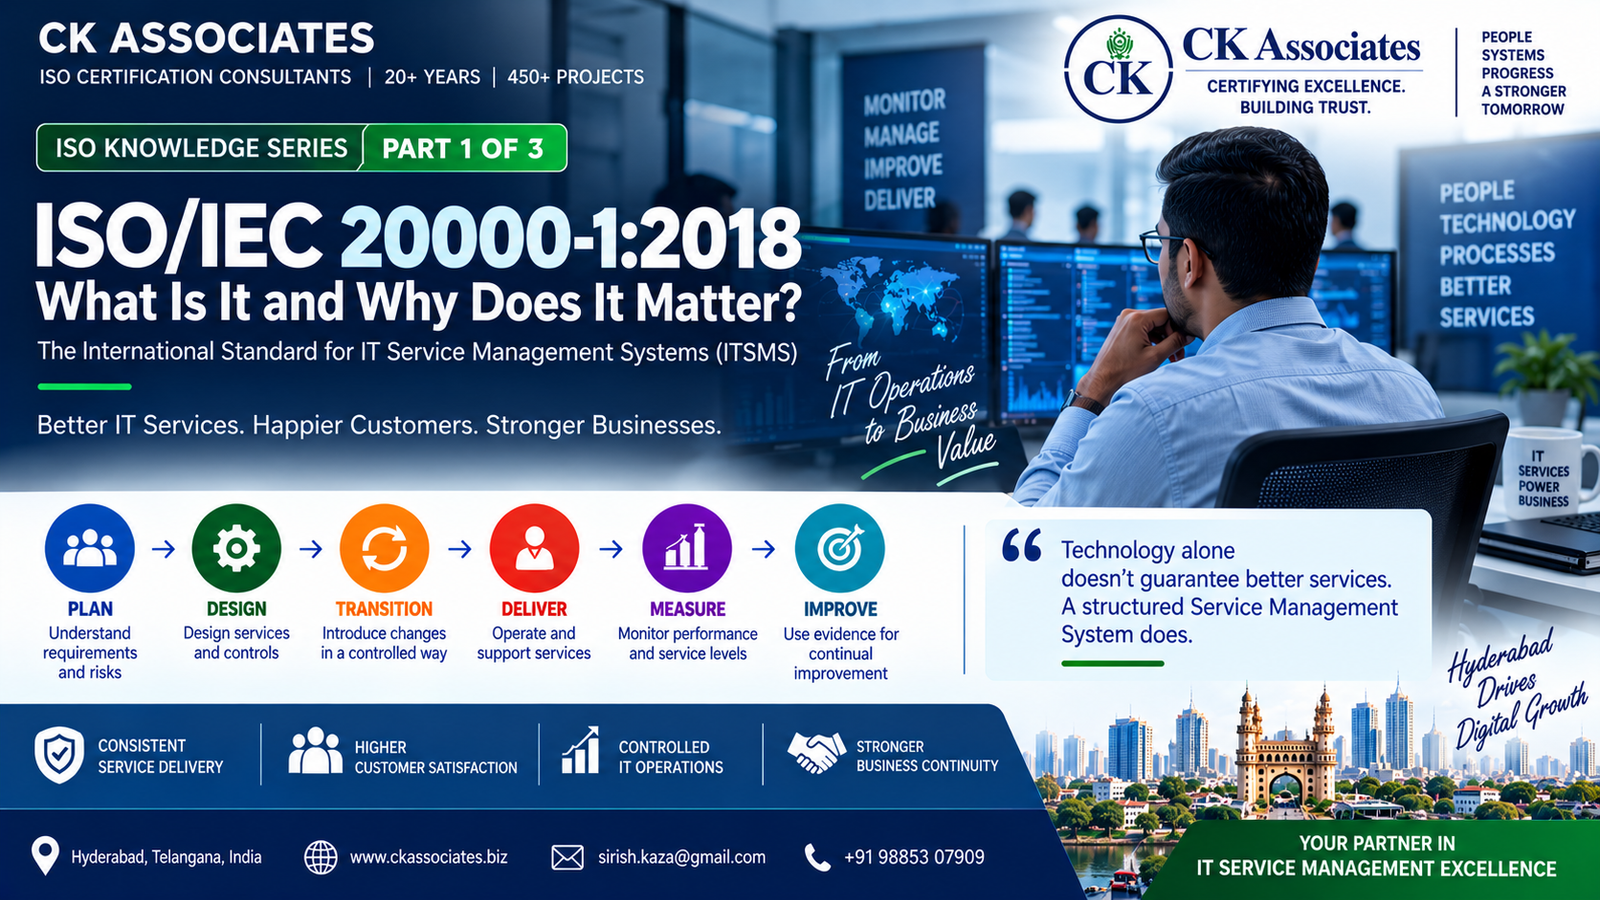
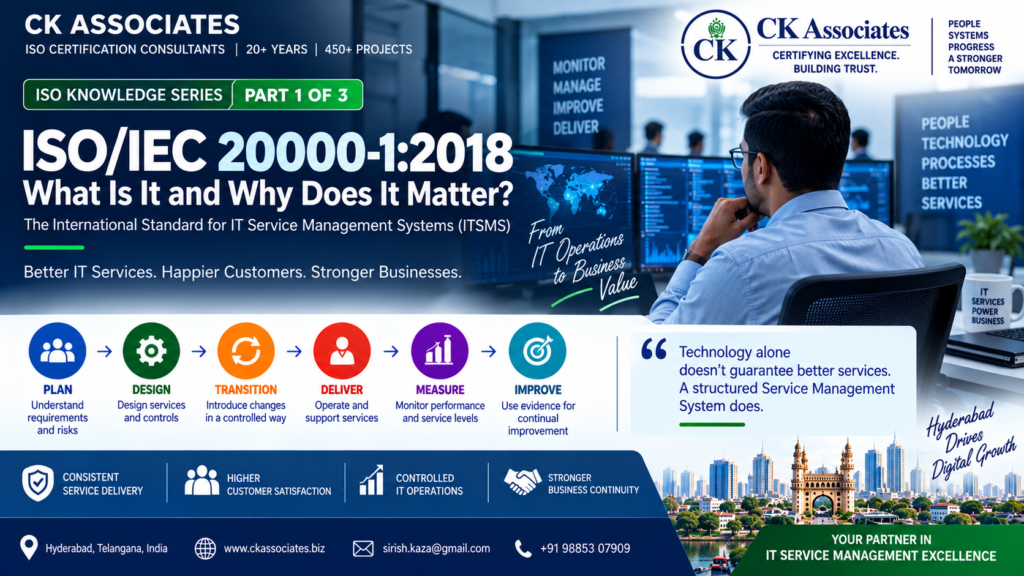
10. The Core Philosophy of ISO/IEC 20000-1
At its heart, ISO/IEC 20000-1 is about consistent, controlled and continually improving service delivery.
A simple model is:
PLAN
Understand:
- customer needs
- service requirements
- risks
- resources
- objectives
↓
DESIGN
Design:
- services
- processes
- controls
- service levels
↓
TRANSITION
Introduce:
- new services
- changed services
- releases
in a controlled manner.
↓
DELIVER
Operate and support services.
↓
MEASURE
Monitor:
- performance
- service levels
- incidents
- customer experience
- process effectiveness
↓
IMPROVE
Use evidence to improve the service-management system.
11. What Does ISO/IEC 20000-1 Focus On?
The standard covers a broad service-management system.
Some important areas include:
Service Management Planning
Establishing the direction and plans for service management.
Service Requirements
Understanding what customers and interested parties require.
Service Design and Transition
Ensuring new or changed services can be introduced in a controlled manner.
Service Delivery
Managing the operational delivery of services.
Relationship Management
Maintaining appropriate relationships with customers and relevant parties.
Service Level Management
Defining and monitoring service expectations and performance.
Service Reporting
Providing useful service-performance information.
Incident Management
Managing interruptions and restoring service.
Service Request Management
Handling defined service requests.
Problem Management
Addressing causes and reducing recurring incidents.
Availability Management
Managing service availability requirements.
Capacity Management
Ensuring resources can support service requirements.
Service Continuity
Preparing for significant disruptions.
Information Security
Managing information-security aspects relevant to service management.
Supplier Management
Managing external suppliers that contribute to service delivery.
Change Management
Controlling changes that can affect services.
Release and Deployment
Managing the introduction of new or changed service components.
These areas will be examined in much greater detail in Part 2.
12. Service Management Is About Value — Not Just Technology
A major shift in modern IT service management is moving away from:
“What technology do we operate?”
toward:
“What value does the service deliver?”
For example, a customer may not care which server model is being used.
They care that:
- the application is available
- transactions work
- support responds quickly
- incidents are resolved
- information is secure
- changes do not unexpectedly disrupt operations
ISO has specifically highlighted the importance of determining what constitutes value for the organization and its customers.
13. Example: SaaS Company
Consider a Hyderabad-based SaaS company serving customers across India and overseas.
Its platform supports 5,000 business users.
The company experiences:
- frequent support tickets
- inconsistent incident priorities
- unplanned production changes
- unclear SLA monitoring
- weak escalation
- limited service reporting
- recurring incidents
Management decides to establish an ISO/IEC 20000-1-based SMS.
The organization starts defining:
Service Catalogue
↓
Service Levels
↓
Incident Management
↓
Problem Management
↓
Change Management
↓
Release Management
↓
Availability
↓
Capacity
↓
Continuity
↓
Supplier Management
↓
Service Reporting
↓
Continual Improvement
The objective isn’t to generate paperwork.
The objective is to make service delivery repeatable, measurable and controllable.
14. Benefits of ISO/IEC 20000-1
A properly implemented SMS can help organizations achieve several benefits.
1. Consistent Service Delivery
Defined processes reduce dependence on individual employees.
2. Better Customer Experience
Customers receive clearer expectations, communication and service management.
3. Improved Incident Management
Structured incident processes can improve response and restoration.
4. Controlled Changes
Changes are assessed and managed rather than introduced randomly.
5. Better Service Performance Measurement
Organizations can establish meaningful service metrics.
6. Stronger Supplier Management
Third-party providers become part of the controlled service environment.
7. Improved Business Continuity
Critical services can be planned around continuity requirements.
8. Greater Customer Confidence
Certification can provide independent evidence that a formal service-management system exists.
9. Better Governance
Management receives structured information about service performance and improvement.
10. Continual Improvement
Service problems can become inputs for systematic improvement.
ISO has highlighted potential benefits including improved efficiency, better use of technology, cost savings and stronger customer service.
15. Does ISO/IEC 20000-1 Apply Only to Large IT Companies?
No.
The scope of an SMS can be defined around the services and organizational activities being managed.
ISO states that an organization in the scope can even be part of a larger organization, such as a department, and can provide services to internal or external customers.
This means the standard can potentially be relevant to:
- Startups
- SaaS companies
- IT SMEs
- MSPs
- Enterprise IT departments
- GCCs
- Cloud providers
- Data centres
- Outsourcing companies
- Shared-service centres
The key consideration is not simply company size.
It is:
What services are being provided, to whom, and how are those services managed?
16. What Does an ISO/IEC 20000-1 Service Management System Look Like?
A simplified SMS can be visualized as:
                 CUSTOMER REQUIREMENTS
                         │
                         ▼
                SERVICE MANAGEMENT
                      POLICY
                         │
                         ▼
                 SERVICE OBJECTIVES
                         │
          ┌──────────────┼──────────────┐
          ▼              ▼              ▼
       SERVICE        SERVICE        SERVICE
       DESIGN        TRANSITION      DELIVERY
          │              │              │
          └──────────────┼──────────────┘
                         ▼
                  SERVICE MONITORING
                         │
                         ▼
                  SERVICE REPORTING
                         │
                         ▼
                   CUSTOMER FEEDBACK
                         │
                         ▼
                 CONTINUAL IMPROVEMENT
This is the basic management-system thinking behind ISO/IEC 20000-1.
17. ISO/IEC 20000-1 Certification — Is It Possible?
Yes.
Unlike frameworks that are primarily guidance-based, ISO/IEC 20000-1 is a requirements standard that can be used for conformity assessment and certification.
ISO notes that the ISO/IEC 20000 series supports certification and provides assurance to customers that services are being effectively managed.
The certification is performed by an independent certification body, not by ISO itself.
This distinction is important:
ISO publishes the standard.
Certification bodies perform certification audits.
18. What ISO/IEC 20000-1 Certification Does Not Mean
Certification does not mean:
❌ Every IT incident will disappear
❌ The organization will never experience downtime
❌ Every service will automatically meet every SLA
❌ The organization has adopted ITIL in its entirety
❌ Technology infrastructure is automatically secure
❌ Every IT process is perfect
Instead, certification provides evidence that the organization’s defined SMS has been assessed against the applicable requirements of the standard.
The real value comes from how effectively the organization operates the system.
19. ISO/IEC 20000-1 and ITSM Tools
Another misconception is:
“We need an expensive ITSM tool before implementing ISO 20000.”
Not necessarily.
Tools can help, but the management system comes first.
An organization needs to understand:
Process → Responsibility → Control → Measurement → Evidence
before selecting technology.
An organization could use:
- commercial ITSM platforms
- open-source platforms
- service desks
- workflow systems
- monitoring tools
- ticketing systems
- integrated enterprise platforms
The tool should support the process.
Not the other way around.
20. What Evidence Might an Auditor Expect?
An auditor may want to see evidence that the SMS actually operates.
For example:
Incident Management
Incident → Ticket → Priority → Assignment → Resolution → Closure
Change Management
Change Request → Assessment → Approval → Implementation → Review
Service Level Management
Requirement → SLA → Measurement → Reporting → Review
Supplier Management
Supplier → Evaluation → Agreement → Performance → Review
Continual Improvement
Problem → Analysis → Improvement Action → Implementation → Effectiveness
This is why ISO/IEC 20000-1 implementation should focus on objective evidence, not just procedures.
21. ISO/IEC 20000-1 for Hyderabad’s IT & Technology Ecosystem
Hyderabad has a large ecosystem of:
- IT companies
- SaaS organizations
- technology startups
- GCCs
- cloud-service organizations
- managed service providers
- software development companies
- IT-enabled services
- enterprise support functions
For organizations serving enterprise customers, ISO/IEC 20000-1 can be particularly relevant when customers expect demonstrable service-management capability.
A technology company may already have excellent engineers and sophisticated systems.
The next maturity step can be establishing a formal, measurable and auditable Service Management System.
This is especially relevant when competing for enterprise contracts where customers ask:
“How do you manage your IT services?”
“How do you control changes?”
“How do you manage incidents?”
“How do you measure service performance?”
“How do you manage service continuity?”
“How do you control third-party suppliers?”
An ISO/IEC 20000-1-based SMS can provide a structured answer.
22. ISO/IEC 20000-1 + ISO 9001 + ISO/IEC 27001
For technology organizations, an Integrated Management System can be particularly powerful.
ISO 9001
Quality Management
↓
ISO/IEC 20000-1
Service Management
↓
ISO/IEC 27001
Information Security
Together:
Quality + Service + Security
This can provide a strong management-system architecture for:
- SaaS companies
- IT service providers
- GCCs
- MSPs
- software companies
- technology-enabled businesses
ISO’s own practical guidance recognizes the possibility of integrating ISO/IEC 20000-1 with ISO 9001 and ISO/IEC 27001.
23. Consultant’s Insight
One of the most common mistakes in ITSM implementation is starting with the question:
“Which ITIL processes do we need?”
A better starting point is:
“What services do we provide, what do our customers require, and what risks could prevent us from delivering those services effectively?”
Then establish:
Service Requirements
↓
Service Scope
↓
Processes
↓
Responsibilities
↓
Controls
↓
Measurements
↓
Evidence
↓
Improvement
This makes ISO/IEC 20000-1 a business-aligned service-management system, rather than a collection of IT procedures.
24. ISO/IEC 20000-1: The Big Picture
The easiest way to remember the standard is:
PLAN THE SERVICE
Understand requirements and risks.
DESIGN THE SERVICE
Define how the service will work.
TRANSITION THE SERVICE
Introduce changes in a controlled manner.
DELIVER THE SERVICE
Operate and support it.
MEASURE THE SERVICE
Monitor performance and customer expectations.
IMPROVE THE SERVICE
Use evidence to continually improve.
That is the heart of service management.
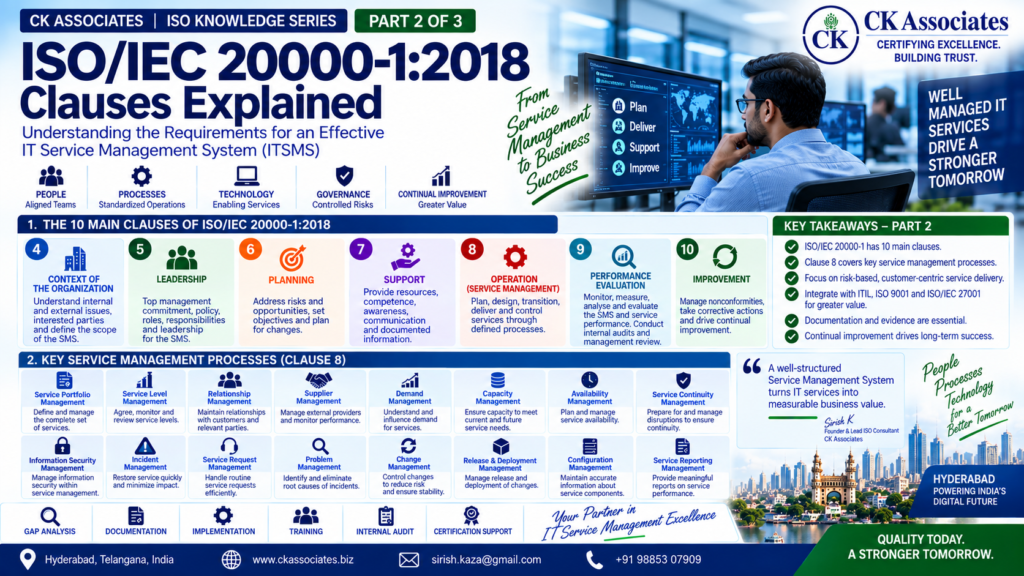
What are the clauses of ISO/IEC 20000-1:2018?
ISO/IEC 20000-1:2018 defines requirements for a Service Management System covering organizational context, leadership, planning, support, service management operations, performance evaluation and improvement. Clauses 4 to 10 form the core requirements, with Clause 8 — Operation of the Service Management System — containing the principal service management processes. These include service portfolio management, service level management, supplier management, demand and capacity management, change management, service design and transition, incident management, service request management, problem management, availability, continuity and information security management. Clauses 9 and 10 then establish mechanisms for monitoring, internal audit, management review, reporting, corrective action and continual improvement.
1. Understanding the Structure of ISO/IEC 20000-1:2018
One of the most important things to understand about ISO/IEC 20000-1 is that the standard is designed as a management system, rather than as a collection of isolated IT processes.
The structure creates a logical chain:
Organizational Context → Leadership → Planning → Support → Operation → Performance Evaluation → Improvement
This means an organization cannot effectively implement ISO 20000 simply by installing an ITSM tool or creating an incident management procedure.
The organization needs to demonstrate that its service management activities are:
- planned;
- controlled;
- supported by competent people;
- documented where required;
- measured;
- reviewed;
- improved.
ISO describes ISO/IEC 20000-1 as requirements for establishing, implementing, maintaining and continually improving an SMS, including planning, design, transition, delivery and improvement of services.
2. Clause 4 — Context of the Organization
Clause 4 establishes the business environment in which the Service Management System operates.
It answers a fundamental question:
What organization and service environment are we actually managing?
Clause 4.1 — Understanding the Organization and Its Context
The organization needs to understand relevant internal and external issues that can affect its ability to achieve the intended outcomes of the SMS.
For an IT service provider, these may include:
- business strategy;
- technology changes;
- customer expectations;
- regulatory requirements;
- cybersecurity threats;
- market competition;
- cloud adoption;
- outsourcing;
- supplier dependencies;
- workforce capabilities;
- financial constraints;
- business continuity requirements.
Example
Consider a SaaS company operating from Hyderabad with customers in India, Europe and the United States.
Its SMS context could include:
- 24×7 service expectations;
- cloud infrastructure dependency;
- international customers;
- data protection requirements;
- service availability commitments;
- third-party hosting providers;
- cybersecurity risks;
- different customer SLAs.
The SMS should reflect this actual operating environment.
Clause 4.2 — Understanding Interested Parties
An organization must identify relevant interested parties and understand their applicable requirements.
These may include:
| Interested Party | Possible Service Requirement |
|---|---|
| Customers | Availability and response times |
| Employees | Competence and clear responsibilities |
| Management | Performance and business value |
| Suppliers | Defined responsibilities |
| Regulators | Applicable compliance |
| Partners | Service integration |
| Internal business units | Reliable internal services |
The important point is that service management is not designed only around the IT department.
It is designed around the services and stakeholders affected by those services.
3. Clause 4.3 — Determining the Scope of the SMS
The organization must establish the scope of its Service Management System.
This is particularly important during certification.
The scope should make clear:
- which services are covered;
- which organizational units are included;
- which locations are included;
- which service management activities are included;
- the boundaries of the SMS;
- relevant interfaces and dependencies.
Example
A company may have:
“Provision of cloud hosting, application support and managed IT infrastructure services from the Hyderabad and Bengaluru operations.”
That is much more meaningful than simply saying:
“IT Services.”
A well-defined scope helps auditors, customers and employees understand what the SMS actually covers.
4. Clause 4.4 — Service Management System
The organization must establish, implement, maintain and continually improve the SMS.
This is where the different elements of ISO 20000 start becoming an integrated management system.
Think of the SMS as the management framework connecting people, processes, technology, suppliers, information and governance.
5. Clause 5 — Leadership
ISO/IEC 20000-1 is not intended to be an IT department’s isolated project.
Top management has an important role.
Clause 5.1 — Leadership and Commitment
Top management needs to demonstrate leadership and commitment toward the SMS.
This includes ensuring that:
- service management objectives support organizational objectives;
- the SMS requirements are integrated into business processes;
- resources are available;
- the importance of effective service management is communicated;
- continual improvement is promoted.
Consultant’s Insight
A common implementation problem is:
“Management wants the certificate, but nobody owns the service management system.”
That approach usually produces documentation without operational maturity.
Effective ISO 20000 implementation starts when management treats service management as a business capability, not merely an audit requirement.
6. Clause 5.2 — Service Management Policy
The organization needs a service management policy appropriate to its purpose and context.
The policy should establish the organization’s direction for service management.
It should be:
- documented;
- communicated;
- understood;
- available to relevant interested parties where appropriate;
- maintained as appropriate.
A good policy should not simply say:
“We are committed to providing quality IT services.”
It should establish a meaningful management direction around service requirements, performance and continual improvement.
7. Clause 5.3 — Roles, Responsibilities and Authorities
People need to know who is responsible for what.
For example:
| Role | Typical Responsibility |
|---|---|
| Top Management | Direction and resources |
| Service Manager | SMS oversight |
| Service Desk Manager | Incident/request operations |
| Change Manager | Change control |
| Problem Manager | Root-cause management |
| Service Level Manager | SLA performance |
| Supplier Manager | Supplier performance |
| Configuration Manager | Configuration information |
| Internal Auditor | Independent assessment |
The exact organizational structure can differ from company to company.
ISO/IEC 20000-1 does not require every organization to use identical job titles.
What matters is that responsibilities and authorities are clearly established and effective.
8. Clause 6 — Planning
Clause 6 brings risk, opportunity and objectives into the SMS.
Clause 6.1 — Actions to Address Risks and Opportunities
The organization needs to determine risks and opportunities that need to be addressed so the SMS can achieve its intended outcomes.
For IT services, examples may include:
Risks
- major system outage;
- cloud provider failure;
- cyberattack;
- loss of key personnel;
- inadequate capacity;
- supplier failure;
- poor change control;
- incomplete configuration information.
Opportunities
- automation;
- self-service portals;
- AI-assisted service desk;
- predictive monitoring;
- cloud optimization;
- process standardization;
- improved service analytics.
Risk management should be connected to actual service management operations.
9. Clause 6.2 — Service Management Objectives
Service management objectives should be established at relevant functions and levels.
Good objectives should be:
- measurable where practicable;
- monitored;
- communicated;
- consistent with the service management policy;
- relevant to service requirements.
Example objectives
Instead of:
“Improve incident management.”
Use a measurable objective such as:
“Improve the percentage of priority incidents resolved within agreed service levels.”
Other examples could include:
- improve SLA compliance;
- reduce recurring incidents;
- reduce average resolution time;
- improve service availability;
- reduce failed changes;
- improve customer satisfaction.
10. Clause 6.3 — Plan the Service Management System
The organization needs a Service Management Plan.
ISO/IEC JTC 1/SC 40 guidance specifically identifies Clause 6.3 as requiring a service management plan and notes that the plan should align with the service management policy, objectives, risks, opportunities and service requirements.
The plan may address or reference:
- SMS scope;
- policy;
- objectives;
- risks and opportunities;
- service requirements;
- resources;
- processes;
- responsibilities;
- measurements;
- operational controls;
- improvement activities.
Important point
The Service Management Plan does not necessarily need to contain every piece of information in one document.
The ISO guidance explains that some required information may be referenced from other documents, systems or tools.
11. Clause 7 — Support of the Service Management System
Even a well-designed SMS will fail if people, resources and information are inadequate.
Clause 7 addresses the supporting infrastructure.
It includes:
- Resources;
- Competence;
- Awareness;
- Communication;
- Documented information;
- Knowledge.
11.1 Resources
The organization needs to determine and provide resources necessary for the SMS and services.
These may include:
- people;
- infrastructure;
- service management tools;
- monitoring systems;
- financial resources;
- technology;
- facilities;
- knowledge resources.
11.2 Competence
People performing work affecting service management need appropriate competence.
Competence can come from:
- education;
- training;
- experience;
- technical skills;
- certifications;
- practical exposure.
Example
An organization cannot expect effective change management simply because it has a change management procedure.
The people performing change management must understand:
- risk assessment;
- approval;
- scheduling;
- testing;
- rollback;
- documentation;
- post-implementation review.
11.3 Awareness
Personnel should understand:
- the service management policy;
- relevant objectives;
- their contribution;
- consequences of not following SMS requirements.
12. Clause 7.4 — Communication
Service management depends heavily on communication.
Communication may occur between:
- IT and customers;
- service desk and technical teams;
- management and service owners;
- organization and suppliers;
- internal teams;
- incident management and business stakeholders.
A major incident with poor communication can create more business damage than the technical failure itself.
13. Clause 7.5 — Documented Information
The organization must control documented information required by the SMS and the standard.
Depending on the organization’s needs, this may include:
- policies;
- procedures;
- service catalogues;
- SLAs;
- service reports;
- audit records;
- incident records;
- change records;
- configuration information;
- supplier records;
- training records;
- management review records;
- corrective action records.
Key principle
ISO 20000 is not about creating documents for the sake of creating documents.
Documentation should support effective service management and provide appropriate evidence.
14. Clause 7.6 — Knowledge
Knowledge is critical to service continuity.
Organizations need to determine and maintain the knowledge required to operate the SMS and services.
Examples include:
- troubleshooting knowledge;
- service architecture;
- known errors;
- configuration knowledge;
- support procedures;
- escalation information;
- supplier contacts;
- recovery procedures;
- lessons learned.
A service desk that depends entirely on one experienced employee creates operational risk.
15. Clause 8 — Operation of the Service Management System
Now we reach the operational core of ISO/IEC 20000-1.
Clause 8 covers the processes used to plan, deliver, control, support and assure services.
The structure includes:
- 8.1 Operational Planning and Control
- 8.2 Service Portfolio
- 8.3 Relationship and Agreement
- 8.4 Supply and Demand
- 8.5 Service Design, Build and Transition
- 8.6 Resolution and Fulfilment
- 8.7 Service Assurance
16. Clause 8.1 — Operational Planning and Control
The organization needs to plan, implement and control the processes required to meet service requirements.
This means operational activities should not depend entirely on informal practices.
Controls should address:
- planned services;
- operational requirements;
- acceptance criteria;
- service performance;
- process controls;
- changes;
- outsourced activities;
- evidence.
17. Clause 8.2 — Service Portfolio
Service portfolio management provides a structured view of the services managed by the organization.
8.2.1 Service Delivery
Services need to be delivered according to established requirements and plans.
8.2.2 Plan the Services
Service planning should consider:
- service requirements;
- resources;
- technology;
- dependencies;
- service levels;
- risks;
- service management objectives.
8.2.3 Control of Parties Involved in the Service Lifecycle
Organizations increasingly rely on:
- cloud providers;
- SaaS platforms;
- hosting providers;
- managed service providers;
- external support organizations.
ISO 20000 requires the organization to control relevant parties involved in the service lifecycle.
18. Clause 8.2.4 — Service Catalogue Management
The service catalogue should provide appropriate information about the services.
For example:
| Service | Description | Availability | SLA |
|---|---|---|---|
| Cloud Hosting | Managed cloud infrastructure | 24×7 | 99.9% |
| Application Support | Business application support | Business hours | 4-hour response |
| Managed Network | Network monitoring and support | 24×7 | Defined SLA |
The catalogue should reflect actual services rather than being merely a marketing document.
19. Clause 8.2.5 — Asset Management
The organization needs appropriate control over assets required to deliver services.
These could include:
- servers;
- network equipment;
- software;
- cloud resources;
- laptops;
- databases;
- licenses;
- service components.
Asset management helps organizations understand what resources support their services.
20. Clause 8.2.6 — Configuration Management
Configuration management is concerned with maintaining appropriate information about configuration items and their relationships.
Examples:
Application → Database → Server → Network → Cloud Platform
If one component changes, the organization should understand what services may be affected.
This becomes particularly important during:
- incident investigation;
- change management;
- impact analysis;
- problem management;
- service continuity planning.
21. Clause 8.3 — Relationship and Agreement
Clause 8.3 focuses on relationships and agreements.
It includes:
- business relationship management;
- service level management;
- supplier management.
21.1 Business Relationship Management
The organization should establish and maintain appropriate relationships with customers and relevant interested parties.
This includes understanding:
- customer needs;
- service expectations;
- feedback;
- changing requirements;
- service performance.
22. Clause 8.3.3 — Service Level Management
Service Level Management is one of the most recognizable areas of ITSM.
It connects service delivery with measurable commitments.
Examples include:
- availability;
- response time;
- resolution time;
- support hours;
- service restoration;
- performance thresholds.
SLA example
A customer might agree to:
Priority 1 incidents: 30-minute response and defined restoration target.
The organization then needs processes and evidence to determine whether it is actually meeting the agreed requirement.
23. Clause 8.3.4 — Supplier Management
Modern IT services frequently depend on external parties.
Supplier management should address relevant suppliers and their ability to support service requirements.
Examples:
- cloud hosting;
- telecom;
- cybersecurity;
- software vendors;
- data centres;
- managed service providers.
Supplier performance should be monitored where relevant.
24. Clause 8.4 — Supply and Demand
Clause 8.4 addresses:
- budgeting and accounting for services;
- demand management;
- capacity management.
Why does this matter?
A service may have excellent technical architecture but still fail if:
Demand exceeds capacity.
For example, an e-commerce platform may normally process 10,000 transactions per hour but receive 50,000 during a major sale.
Capacity planning and demand management become business-critical.
25. Clause 8.5 — Service Design, Build and Transition
This section addresses what happens when services are:
- created;
- modified;
- tested;
- transitioned;
- released.
It includes:
8.5.1 Change Management
Changes need to be controlled to reduce unintended impact.
A typical change lifecycle includes:
Request → Assess → Approve → Plan → Implement → Review
Not every change carries the same risk, so organizations should apply appropriate controls.
25.1 Service Design and Transition
New or changed services should be designed and transitioned in a controlled manner.
Consider:
- service requirements;
- acceptance criteria;
- resources;
- support readiness;
- documentation;
- security;
- continuity;
- monitoring;
- training.
25.2 Release and Deployment Management
Release and deployment management controls how new or changed service components move into the operational environment.
The objective is not simply:
“Deploy quickly.”
It is:
Deploy predictably, safely and with appropriate controls.
26. Clause 8.6 — Resolution and Fulfilment
This section covers three highly visible ITSM processes:
- Incident Management
- Service Request Management
- Problem Management
26.1 Incident Management
The objective is to manage incidents and restore normal service as effectively as possible.
Examples:
- email outage;
- application failure;
- network interruption;
- database failure;
- login failure.
Incident management asks:
How quickly can we restore the affected service?
26.2 Service Request Management
Service requests are generally different from incidents.
Examples:
- password reset;
- access request;
- software installation;
- new user account;
- standard information request.
A structured request process improves consistency and efficiency.
27. Problem Management
Problem management looks beyond individual incidents.
It asks:
Why does this keep happening?
For example:
Incident
Application crashes every Monday morning.
Problem Management
Investigation identifies a recurring resource saturation issue.
Improvement
Capacity or architecture is changed to remove the underlying cause.
This is how incident data can become improvement intelligence.
28. Clause 8.7 — Service Assurance
Clause 8.7 includes:
- Service Availability Management;
- Service Continuity Management;
- Information Security Management.
28.1 Service Availability Management
Availability management focuses on ensuring services are available according to agreed requirements.
Measures may include:
- uptime;
- downtime;
- availability percentage;
- service interruptions;
- recurring outages.
28.2 Service Continuity Management
Service continuity addresses the organization’s ability to continue or recover services when disruptive events occur.
Potential scenarios include:
- major infrastructure failure;
- cyber incident;
- natural disaster;
- cloud outage;
- data centre disruption;
- loss of critical resources.
A continuity plan should be supported by appropriate preparation and testing.
29. Information Security Management
ISO/IEC 20000-1 includes information security management within its service assurance requirements.
This is where ISO 20000 and ISO/IEC 27001 can complement each other.
ISO/IEC 20000 focuses on service management.
ISO/IEC 27001 focuses on information security management.
An organization may integrate the two systems where appropriate.
ISO’s service management community specifically notes that ISO/IEC 20000-1 can complement other standards and frameworks, including ISO/IEC 27001 and IT service management frameworks.
30. Clause 9 — Performance Evaluation
Implementation is not complete simply because processes exist.
The organization must determine whether those processes are actually working.
Clause 9 includes:
- monitoring, measurement, analysis and evaluation;
- internal audit;
- management review;
- service reporting.
30.1 Clause 9.1 — Monitoring, Measurement, Analysis and Evaluation
The organization needs to determine:
- what should be monitored;
- what should be measured;
- how measurements are performed;
- when measurements are performed;
- when results are analysed;
- how effectiveness is evaluated.
Potential ITSM KPIs include:
- SLA compliance;
- incident response;
- incident resolution;
- service availability;
- customer satisfaction;
- failed changes;
- recurring incidents;
- service request turnaround;
- capacity utilization.
The important principle is:
Measure what matters to the services and the business.
31. Clause 9.2 — Internal Audit
Internal audits provide an independent assessment of whether the SMS:
- conforms to organizational requirements;
- conforms to ISO/IEC 20000-1 requirements;
- is effectively implemented;
- is maintained.
An internal audit should not become a document-checking exercise.
A strong auditor examines:
Requirement → Process → Evidence → Effectiveness
For example:
If the organization claims that all major changes require approval, the auditor should examine actual change records rather than simply checking whether a change procedure exists.
32. Clause 9.3 — Management Review
Management review provides top management with an opportunity to evaluate the continuing suitability, adequacy and effectiveness of the SMS and services.
Inputs can include:
- audit results;
- service performance;
- customer feedback;
- objectives;
- supplier performance;
- resource requirements;
- risks and opportunities;
- changes affecting the SMS;
- improvement opportunities.
The output should lead to decisions and actions where necessary.
33. Clause 9.4 — Service Reporting
Service reporting converts operational data into management information.
Reports may show:
- SLA performance;
- incidents;
- service requests;
- availability;
- customer satisfaction;
- trends;
- supplier performance;
- capacity;
- improvement actions.
ISO/IEC 20000-1 requires service reporting to address performance and effectiveness and to include trends.
Consultant’s Insight
A dashboard full of numbers is not automatically a useful service report.
The real question is:
What decision can management make from this information?
34. Clause 10 — Improvement
Clause 10 ensures the SMS does not remain static.
It covers:
- nonconformity and corrective action;
- continual improvement.
35. Clause 10.1 — Nonconformity and Corrective Action
When something goes wrong, the organization should:
- react to the nonconformity;
- control and correct it;
- address consequences;
- determine whether corrective action is required;
- identify relevant causes;
- implement appropriate action;
- review effectiveness.
Example
If repeated SLA breaches occur, simply closing each individual incident is not enough.
The organization should investigate why the breaches are recurring.
Possible causes could include:
- insufficient staffing;
- poor capacity planning;
- inadequate monitoring;
- unrealistic SLA;
- supplier failure;
- weak escalation;
- inadequate process controls.
36. Clause 10.2 — Continual Improvement
Continual improvement is one of the central principles of the management system.
Improvement may involve:
- process changes;
- automation;
- better monitoring;
- service redesign;
- improved capacity;
- supplier improvement;
- employee training;
- technology upgrades;
- risk reduction;
- customer experience improvements.
The objective is not to change everything continuously.
It is to make controlled, evidence-based improvements that increase the effectiveness of the SMS and services.
ISO/IEC 20000-1:2018 — Clause Structure at a Glance
| Clause | Main Focus | Practical Question |
|---|---|---|
| 4 | Context | What services and environment are we managing? |
| 5 | Leadership | Who provides direction and accountability? |
| 6 | Planning | What risks, objectives and plans exist? |
| 7 | Support | Do we have people, resources and information? |
| 8 | Operation | Are services planned, delivered and controlled? |
| 9 | Performance Evaluation | Are we measuring and reviewing performance? |
| 10 | Improvement | Are we correcting problems and improving? |
The Heart of ISO 20000: Clause 8
If you remember only one thing from this article, remember this:
Clause 8 connects the management system to the actual delivery and control of services.
Its major process groups can be visualized as:
Service Portfolio
↓
Relationships & Agreements
↓
Supply & Demand
↓
Service Design, Build & Transition
↓
Resolution & Fulfilment
↓
Service Assurance
This creates a lifecycle-oriented approach to service management.
ISO 20000-1 vs ITIL — Are They the Same?
No.
This distinction is important.
| ISO/IEC 20000-1 | ITIL |
|---|---|
| International standard | Service management framework/practice guidance |
| Contains requirements | Provides recommended practices |
| Can support certification | ITIL itself is not an ISO conformity standard |
| Defines management-system requirements | Provides practical service management guidance |
| Focuses on conformity and effectiveness | Focuses on practices and value creation |
ISO itself describes ISO/IEC 20000-1 as a requirements standard and notes that it is complementary to service management frameworks such as ITIL.
Therefore:
ITIL can help an organization implement effective ITSM practices, while ISO/IEC 20000-1 provides requirements against which the SMS can be assessed.
ISO 20000-1 + ISO 9001 + ISO/IEC 27001
Organizations often consider integrating these standards.
ISO 9001
Focus:
Quality Management
ISO/IEC 20000-1
Focus:
Service Management
ISO/IEC 27001
Focus:
Information Security Management
For an IT company, SaaS provider or GCC, these systems can potentially share common infrastructure such as:
- document control;
- internal audit;
- management review;
- corrective action;
- risk management;
- competence;
- training;
- supplier management;
- continual improvement.
However, integration should not mean assuming that one standard automatically satisfies all requirements of another.
Each standard has its own requirements and intended outcomes.
What Evidence Might an ISO 20000 Auditor Look For?
One of the biggest differences between having an ITSM process and demonstrating conformity is evidence.
Examples of evidence can include:
Service Management
- SMS scope;
- service management policy;
- service management plan;
- objectives;
- service catalogue.
Service Level Management
- SLAs;
- service reports;
- SLA performance;
- customer reviews.
Incident Management
- incident tickets;
- priority definitions;
- escalation records;
- resolution records.
Change Management
- change requests;
- impact assessment;
- approval;
- implementation evidence;
- post-change review.
Problem Management
- problem records;
- root-cause analysis;
- corrective actions;
- known error information.
Supplier Management
- supplier evaluations;
- contracts;
- performance reviews;
- supplier-related incidents.
Internal Audit
- audit programme;
- audit plans;
- findings;
- corrective actions;
- closure evidence.
Management Review
- agenda;
- inputs;
- decisions;
- actions;
- follow-up.
Common ISO 20000 Implementation Mistakes
1. Treating ISO 20000 as an IT Help Desk Standard
It is much broader than incident management.
2. Buying an ITSM Tool and Assuming Compliance
A tool can enable processes.
It does not automatically create a compliant SMS.
3. Writing Procedures That Nobody Uses
Auditors will eventually compare documented processes with operational evidence.
4. Ignoring Suppliers
Cloud, hosting, telecom and other external providers can materially affect service delivery.
5. Measuring Everything
Too many meaningless KPIs can hide the metrics that actually matter.
6. Ignoring Customer Requirements
Service management should ultimately support agreed service requirements and value delivery.
7. Treating Internal Audit as a Formality
Internal audit should identify weaknesses before they become certification or operational problems.
8. Forgetting Continual Improvement
The SMS should evolve as services, technology, risks and customer expectations change.
Practical Example: SaaS Company Implementing ISO 20000-1
Consider a Hyderabad-based SaaS company serving enterprise customers.
Before implementation, it may have:
- a service desk;
- cloud infrastructure;
- informal escalation;
- customer SLAs;
- development teams;
- monitoring tools;
- outsourced cloud services.
But its processes may not be consistently controlled.
After implementing an SMS
The organization establishes:
Service Catalogue
→ What services are offered?
SLA Management
→ What has been promised?
Incident Management
→ How are disruptions handled?
Problem Management
→ Why do recurring incidents happen?
Change Management
→ How are changes controlled?
Configuration Management
→ What components support services?
Supplier Management
→ How are external providers controlled?
Service Reporting
→ How is performance demonstrated?
Management Review
→ What does management need to improve?
This is where ISO/IEC 20000-1 moves from being a certification project to becoming an operational management system.
ISO/IEC 20000-1 Certification Readiness: Part 2 Checklist
Before moving toward certification, an organization should be able to answer yes to questions such as:
Context
- Have we defined our SMS scope?
- Have we identified relevant interested parties?
- Do we understand our service environment?
Leadership
- Is there management commitment?
- Is there a service management policy?
- Are responsibilities defined?
Planning
- Have we identified risks and opportunities?
- Are service management objectives established?
- Is there a service management plan?
Support
- Are competent resources available?
- Are people aware of their responsibilities?
- Is documented information controlled?
- Is required knowledge available?
Operations
- Is there a service portfolio?
- Is the service catalogue controlled?
- Are SLAs managed?
- Are suppliers controlled?
- Are demand and capacity managed?
- Are changes controlled?
- Are incidents and requests managed?
- Are problems analysed?
- Is service availability addressed?
- Is service continuity addressed?
- Is information security addressed?
Evaluation
- Are KPIs measured?
- Are internal audits conducted?
- Is management review performed?
- Are service reports generated?
Improvement
- Are nonconformities controlled?
- Is corrective action implemented?
- Is continual improvement demonstrated?
Consultant’s Insight — What Auditors Really Want to See
At CK Associates, one of the most important practical principles we emphasize during management-system implementation is:
A process is not mature merely because it is documented; it becomes credible when people consistently operate it and the organization can demonstrate evidence of its effectiveness.
For ISO/IEC 20000-1, this means the implementation team should avoid building a collection of procedures that exist only for the certification audit.
Instead, the SMS should connect:
Business Requirements → Service Requirements → Processes → Technology → People → Measurements → Evidence → Improvement
That chain is what turns IT service management into a management system.
Why ISO/IEC 20000-1 Matters for Modern IT Businesses
The nature of IT services has changed significantly.
Organizations now depend on:
- cloud platforms;
- SaaS;
- APIs;
- remote support;
- managed services;
- DevOps;
- automation;
- cybersecurity;
- global service delivery;
- third-party platforms.
A service failure can affect customers, revenue, reputation and business continuity.
ISO/IEC 20000-1 provides a structured framework for managing these service expectations.
ISO also notes that the standard can be applied by organizations of different types and sizes and is complementary to other service management frameworks and standards.
How do you implement ISO/IEC 20000-1:2018?
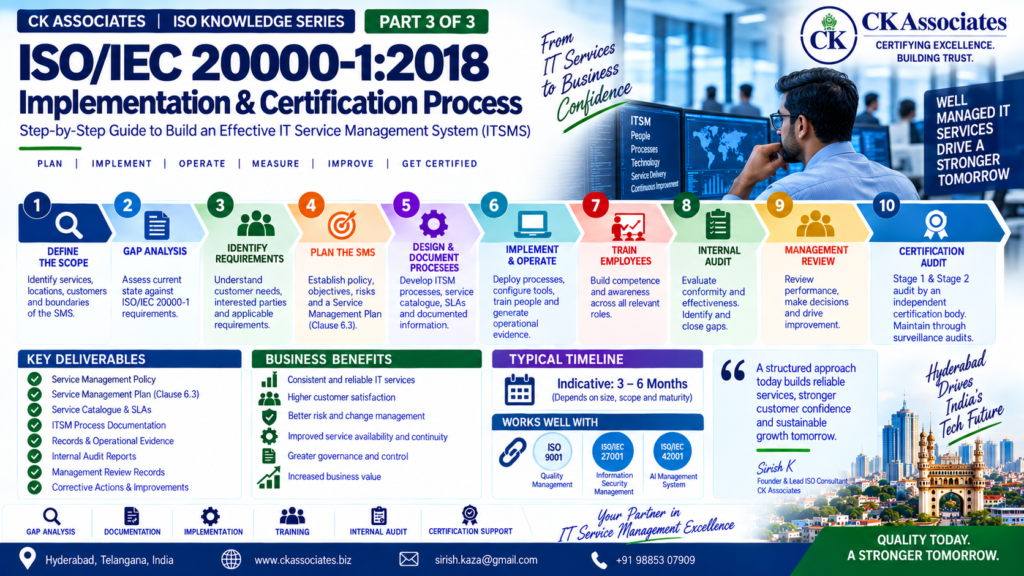
ISO/IEC 20000-1 implementation normally begins by defining the Service Management System scope and understanding customer, service and organizational requirements. The organization then performs a gap analysis, establishes its service management policy and objectives, develops the Service Management Plan, defines service management processes, establishes appropriate documentation and controls, trains personnel, operates the SMS, collects evidence, conducts internal audits, performs management review and addresses identified gaps before engaging an independent certification body. ISO/IEC 20000-1 requires the organization to establish, implement, maintain and continually improve the SMS; ISO’s own guidance also identifies Clause 6.3 as requiring a Service Management Plan.
1. First Understand What You Are Certifying
Before beginning implementation, an organization must answer a fundamental question:
What exactly will the ISO/IEC 20000-1 Service Management System cover?
This is the starting point for the entire project.
ISO/IEC 20000-1 is designed around an SMS and the services within its defined scope. ISO notes that the standard can be used by organizations demonstrating their service-management capability, monitoring and reviewing an SMS, improving service management, or undergoing conformity assessment.
The scope could cover:
- an IT service provider;
- a SaaS business;
- a managed service provider;
- a cloud service operation;
- an internal IT department;
- a GCC;
- a shared service organization;
- a data-centre operation;
- a specific business unit;
- selected services rather than every service the organization provides.
2. Define the ISO 20000 Scope
Scope definition is one of the most important implementation decisions.
A weak scope may be:
“IT Services.”
A stronger scope identifies:
- organization;
- service locations;
- services;
- service users/customers;
- relevant infrastructure;
- service management activities;
- organizational boundaries.
Example
“Provision of cloud infrastructure, application hosting, service desk and managed IT support services from the organization’s Hyderabad operations.”
This immediately provides greater clarity.
Why Scope Matters
The scope affects:
- implementation effort;
- documentation;
- service catalogue;
- processes;
- audit activities;
- certification audit;
- employee involvement;
- evidence requirements;
- certification cost.
If the scope is too broad, implementation can become unnecessarily complex.
If the scope is too narrow, it may not provide the business value the organization actually needs.
Consultant’s Insight
Do not select the certification scope simply because it sounds impressive.
Select a scope that is:
accurate, defensible, operationally manageable and commercially meaningful.
3. Conduct an ISO/IEC 20000-1 Gap Analysis
Once the scope is defined, the next step should normally be a gap analysis.
The purpose is to compare the organization’s current service management arrangements with ISO/IEC 20000-1 requirements.
A gap assessment may examine:
- SMS scope;
- service management policy;
- service objectives;
- service requirements;
- service catalogue;
- service portfolio;
- SLA management;
- relationship management;
- supplier management;
- demand management;
- capacity management;
- availability;
- continuity;
- information security;
- incident management;
- service request management;
- problem management;
- change management;
- release and deployment;
- configuration management;
- service reporting;
- internal audit;
- management review;
- corrective action;
- continual improvement.
4. Use a Practical Gap Matrix
A useful gap-analysis matrix can look like this:
| Requirement Area | Current State | Gap | Action | Owner | Target |
|---|---|---|---|---|---|
| SMS Scope | Partially defined | Scope boundaries unclear | Define scope | SMS Manager | Week 1 |
| Service Catalogue | Exists | Incomplete | Update catalogue | Service Manager | Week 2 |
| SLA Management | Informal | No consistent review | Establish SLA process | SLM | Week 3 |
| Incident Management | Implemented | KPI evidence weak | Define reporting | Service Desk | Week 3 |
| Change Management | Tool-based | Approval inconsistent | Strengthen controls | Change Manager | Week 4 |
| Internal Audit | Not established | Audit programme missing | Develop programme | Internal Auditor | Week 8 |
This converts the standard from an abstract set of requirements into an implementation roadmap.
5. Establish the Service Management Policy
The organization should establish a service management policy appropriate to its purpose and context.
The policy should provide management direction for the SMS.
It should connect service management with:
- business objectives;
- customer requirements;
- service quality;
- compliance;
- risk management;
- performance;
- continual improvement.
Avoid a Generic Policy
A weak policy might say:
“We are committed to providing excellent IT services.”
A more useful policy establishes commitments around:
- meeting agreed service requirements;
- maintaining effective service management processes;
- managing service risks;
- monitoring performance;
- developing competence;
- continually improving the SMS.
6. Establish Service Management Objectives
Objectives convert the policy into measurable direction.
Examples include:
Service Availability
Maintain agreed availability levels for critical services.
Incident Management
Improve the percentage of priority incidents resolved within agreed targets.
Change Management
Reduce unsuccessful or unauthorized changes.
Customer Satisfaction
Improve customer satisfaction based on defined measurement methods.
Service Requests
Reduce turnaround time for standard service requests.
Supplier Management
Improve supplier SLA performance.
The exact objectives should be based on the organization’s services and business priorities.
7. Develop the Service Management Plan
This is a particularly important ISO 20000 requirement.
ISO/IEC 20000-1 Clause 6.3 requires a Service Management Plan. ISO/IEC JTC 1/SC 40’s published guidance explains that the plan needs to consider the service management policy, objectives, risks and opportunities, service requirements and the requirements of ISO/IEC 20000-1; it also explains that the plan can reference information maintained in other documents or tools rather than duplicating everything.
The Service Management Plan may address:
- SMS scope;
- service management policy;
- objectives;
- service requirements;
- risks and opportunities;
- organizational responsibilities;
- resources;
- service management processes;
- technology;
- measurement;
- reporting;
- internal audit;
- management review;
- continual improvement.
8. Build the ITSM Process Architecture
At this point, the organization moves from planning into implementation.
The organization should define how its service management processes interact.
A simplified architecture could be:
Customer Requirements
↓
Service Portfolio
↓
Service Catalogue
↓
Service Level Management
↓
Service Delivery
↓
Incident / Request / Problem Management
↓
Change / Release / Configuration Management
↓
Availability / Continuity / Information Security
↓
Measurement & Reporting
↓
Management Review
↓
Continual Improvement
This prevents individual processes from becoming disconnected silos.
9. Develop the Service Catalogue
The service catalogue is one of the most useful operational outputs of an ITSM implementation.
It should provide a clear understanding of the services being managed.
For example:
| Service | Customer | Support | Availability | SLA |
|---|---|---|---|---|
| Cloud Hosting | Enterprise Customers | 24×7 | Defined | SLA-A |
| Application Support | Business Users | Business Hours | Defined | SLA-B |
| Managed Network | Internal/External | 24×7 | Defined | SLA-C |
| Service Desk | Employees | Business Hours | Defined | SLA-D |
The catalogue should correspond to actual operational services.
10. Define Service Requirements
Service requirements should be understood before designing service controls.
Requirements may come from:
- customers;
- contracts;
- SLAs;
- business units;
- regulations;
- internal policies;
- suppliers;
- service owners;
- security requirements;
- continuity requirements.
The implementation team should ask:
What does the customer actually require from this service?
Then ask:
What controls are necessary to consistently deliver it?
11. Implement Service Level Management
Service Level Management translates requirements into measurable commitments.
This may involve:
- SLA development;
- service-level targets;
- monitoring;
- reporting;
- customer reviews;
- escalation;
- service improvement.
Example
A SaaS organization may define:
- support hours;
- priority classifications;
- response targets;
- restoration targets;
- availability targets;
- escalation mechanisms.
The organization must then collect evidence demonstrating actual performance.
12. Implement Incident Management
Incident management should define how service disruptions are handled.
A typical process could be:
Incident Reported
↓
Logged
↓
Categorized
↓
Prioritized
↓
Assigned
↓
Investigated
↓
Resolved
↓
Verified
↓
Closed
The organization should define appropriate:
- priority levels;
- escalation rules;
- response targets;
- communication requirements;
- closure criteria;
- reporting.
13. Implement Service Request Management
Service requests should be distinguished from incidents.
Examples include:
- password reset;
- access request;
- software installation;
- account creation;
- standard information request;
- equipment request.
Standardizing these requests can improve:
- turnaround time;
- user experience;
- automation;
- reporting;
- resource efficiency.
14. Implement Problem Management
Problem management should focus on recurring or significant underlying causes.
For example:
Incident Pattern
The same application crashes repeatedly.
Problem Investigation
Root cause:
Database connection pool exhaustion.
Corrective Action
Configuration and capacity are changed.
Result
Recurring incidents decline.
This creates a direct link between operational data and continual improvement.
15. Implement Change Management
Change management controls changes that can affect services.
A practical workflow can include:
Request
→
Impact Assessment
→
Risk Assessment
→
Approval
→
Scheduling
→
Implementation
→
Validation
→
Closure
Changes should be proportionate to their risk.
A low-risk standard change does not necessarily need the same level of control as a high-risk infrastructure change.
16. Implement Release and Deployment Management
Release and deployment processes help ensure that new or changed services enter production in a controlled manner.
Controls may include:
- release planning;
- testing;
- acceptance criteria;
- deployment authorization;
- rollback planning;
- communication;
- post-deployment review.
The objective is not simply faster deployment.
It is controlled and predictable service transition.
17. Implement Configuration Management
The organization should understand the configuration items and relationships necessary to deliver services.
For example:
Customer Application
↓
Application Server
↓
Database
↓
Cloud Infrastructure
↓
Network
↓
External Provider
If a database changes, the organization should understand which services may be affected.
Configuration information therefore supports:
- incident management;
- change management;
- problem management;
- impact analysis;
- continuity planning.
18. Implement Availability Management
Availability management should connect service requirements with actual performance.
The organization should understand:
- required availability;
- actual availability;
- planned downtime;
- unplanned downtime;
- recurring outages;
- critical dependencies.
Example
If a customer contract requires a particular availability target, the organization needs a reliable method for:
- measuring availability;
- calculating performance;
- reporting results;
- investigating failures;
- improving performance.
19. Implement Service Continuity Management
Service continuity is essential for organizations delivering business-critical services.
The organization should identify:
- critical services;
- dependencies;
- continuity requirements;
- disruption scenarios;
- recovery arrangements;
- responsibilities;
- communication;
- testing requirements.
ISO’s published implementation guidance identifies the Service Continuity Plan as another mandatory plan within ISO/IEC 20000-1.
20. Implement Information Security Management
Service management and information security increasingly overlap.
An organization may need controls addressing:
- access;
- confidentiality;
- integrity;
- availability;
- security incidents;
- supplier security;
- service continuity;
- information handling.
For organizations already implementing ISO/IEC 27001, there may be opportunities to integrate common management-system elements while maintaining the distinct requirements of each standard.
21. Supplier Management
Many modern IT services depend on third parties.
Examples include:
- AWS/Azure/cloud providers;
- data centres;
- telecom providers;
- software vendors;
- cybersecurity providers;
- managed service providers;
- SaaS platforms.
The organization should understand which suppliers are critical to service delivery.
Supplier management can include:
- supplier selection;
- requirements;
- agreements;
- performance monitoring;
- review;
- escalation;
- corrective action.
22. Capacity and Demand Management
An effective IT service may fail when demand suddenly exceeds capacity.
Examples:
- seasonal traffic;
- product launches;
- financial-year processing;
- e-commerce events;
- customer onboarding spikes;
- large data workloads.
Capacity management should therefore consider:
Current Demand + Forecast Demand + Available Capacity + Required Capacity
This allows the organization to identify capacity risks before they become service failures.
23. Establish Service Reporting
Service reporting converts operational data into management information.
Reports can cover:
- SLA performance;
- incidents;
- service requests;
- availability;
- customer satisfaction;
- changes;
- problems;
- supplier performance;
- capacity;
- continuity;
- improvement actions.
A good service report should answer:
What happened?
Why did it happen?
Is performance acceptable?
What action is required?
24. Establish ITSM KPIs
A practical ISO 20000 implementation should identify meaningful KPIs.
| Area | Example KPI |
|---|---|
| Service Desk | First response performance |
| Incident | Resolution within target |
| SLA | SLA compliance percentage |
| Availability | Service availability |
| Change | Successful change rate |
| Problem | Recurring incident reduction |
| Request | Average fulfilment time |
| Customer | Satisfaction score |
| Supplier | Supplier SLA performance |
| Capacity | Capacity utilization |
| Continuity | Test completion / effectiveness |
Do not create dozens of KPIs merely because the dashboard can display them.
Measure what helps management make decisions.
25. Establish Documented Information
The documentation structure should reflect the organization’s actual SMS.
Depending on scope and organizational needs, documentation/evidence may include:
Management System
- SMS scope;
- policy;
- objectives;
- Service Management Plan;
- roles and responsibilities.
Service Management
- service catalogue;
- service portfolio;
- service requirements;
- SLAs;
- service reports.
Operational Processes
- incident management;
- service request management;
- problem management;
- change management;
- release and deployment;
- configuration management;
- availability;
- continuity;
- supplier management.
Assurance
- KPI records;
- internal audit;
- management review;
- corrective action;
- improvement records.
Important Principle
ISO 20000 does not mean producing hundreds of documents just to satisfy an auditor.
ISO’s own Service Management Plan guidance specifically recognizes that required information can sometimes be referenced from other documents or tools rather than duplicated inside one master document.
26. Configure or Improve the ITSM Tool
An organization does not necessarily need a particular ITSM software product to implement ISO/IEC 20000-1.
Existing tools may include:
- service desk platforms;
- ticketing systems;
- CMDB/configuration tools;
- monitoring platforms;
- asset-management systems;
- knowledge bases;
- reporting dashboards;
- workflow automation.
The important question is:
Does the technology support the required process and provide appropriate evidence?
Not:
Which software has the most features?
27. Train Employees
Training should be role-specific.
Top Management
Needs to understand:
- SMS objectives;
- responsibilities;
- performance;
- risks;
- improvement.
Service Desk
Needs to understand:
- incident management;
- service requests;
- escalation;
- customer communication.
Change Managers
Need to understand:
- risk;
- impact;
- authorization;
- implementation;
- review.
Service Owners
Need to understand:
- service requirements;
- SLA;
- performance;
- risks;
- improvement.
Internal Auditors
Need to understand:
- ISO/IEC 20000-1 requirements;
- audit methodology;
- evidence evaluation;
- nonconformity;
- corrective action.
28. Operate the SMS Before Certification
This is one of the most important practical stages.
Do not build the system and immediately schedule the certification audit.
The organization needs to operate the system and generate evidence.
Examples:
- incidents are actually logged;
- changes are actually approved;
- SLAs are actually monitored;
- supplier performance is actually reviewed;
- service reports are actually produced;
- internal audits are actually performed;
- management review actually takes place;
- corrective actions are actually tracked.
This is where the SMS becomes real.
29. Conduct an Internal Audit
The internal audit should evaluate whether the SMS:
- conforms to applicable requirements;
- is implemented;
- is maintained;
- is effective.
The audit should examine objective evidence.
For example, don’t merely ask:
“Do you have a change management procedure?”
Ask:
“Show me how the last five significant changes were assessed, approved, implemented and closed.”
That is a much stronger audit approach.
30. Perform Management Review
Management review should evaluate the performance and continuing suitability of the SMS.
Possible inputs include:
- audit results;
- customer feedback;
- SLA performance;
- service performance;
- objectives;
- supplier performance;
- risks;
- resource requirements;
- incidents;
- improvement opportunities.
Outputs can include:
- decisions;
- actions;
- resource requirements;
- improvement initiatives;
- changes to objectives.
31. Close Nonconformities Before Certification
Internal audit may identify:
- major gaps;
- minor gaps;
- observations;
- opportunities for improvement.
The organization should:
- identify the issue;
- correct it where necessary;
- investigate the cause;
- implement corrective action;
- verify effectiveness;
- retain appropriate evidence.
Example
Finding: Several changes were implemented without documented approval.
Root cause: Change approval workflow was not configured correctly.
Correction: Review affected changes.
Corrective action: Configure approval workflow and train change owners.
Effectiveness check: Review subsequent change records.
This is much stronger than simply changing the procedure.
32. Certification Audit — What Happens?
Once the organization considers itself ready, it can engage an independent certification body.
A management-system certification audit is commonly conducted in stages.
Stage 1
Stage 1 generally focuses on readiness and the management system’s design, including matters such as:
- scope;
- documented information;
- organizational context;
- readiness;
- understanding of key processes;
- audit planning.
Stage 2
Stage 2 is the main conformity assessment of the implemented management system.
Auditors examine whether the SMS is:
- implemented;
- effective;
- maintained;
- supported by evidence;
- conforming to applicable requirements.
The exact audit arrangements are determined by the certification body and applicable certification rules.
33. Certification Audit Evidence
Auditors may sample evidence such as:
Service Management
- scope;
- policy;
- objectives;
- Service Management Plan.
Customer Management
- customer requirements;
- SLAs;
- service reviews;
- complaints/feedback.
Operations
- incidents;
- service requests;
- problems;
- changes;
- releases;
- configuration information.
Suppliers
- supplier evaluations;
- contracts;
- performance.
Performance
- KPI reports;
- service reports;
- trend analysis.
Governance
- internal audit;
- management review;
- corrective actions.
The auditor is essentially asking:
Does the implemented system work as described, and can the organization demonstrate it?
34. What Happens If the Auditor Finds Nonconformities?
Nonconformities are not unusual in management-system audits.
What matters is how the organization responds.
A typical response involves:
Finding
↓
Correction
↓
Root Cause Analysis
↓
Corrective Action
↓
Evidence
↓
Effectiveness Review
The certification body’s rules determine how findings affect the certification decision and what follow-up is required.
35. Certification Is Not the End
One of the biggest misconceptions about ISO certification is:
“Once we receive the certificate, the project is finished.”
It is not.
Certification creates an ongoing management-system commitment.
The organization must continue to:
- operate processes;
- monitor performance;
- conduct internal audits;
- conduct management reviews;
- address nonconformities;
- improve services;
- maintain relevant documented information;
- prepare for surveillance/follow-up audits according to the certification body’s programme.
36. ISO 20000 Certification Timeline
There is no universal implementation duration.
The timeline depends on:
- organization size;
- number of services;
- number of locations;
- existing ITSM maturity;
- existing ISO systems;
- complexity of infrastructure;
- number of suppliers;
- service criticality;
- availability of employees;
- quality of existing documentation;
- ITSM tool maturity.
Practical Implementation Phases
A project may be organized approximately as:
| Phase | Typical Activity |
|---|---|
| Phase 1 | Scope & Gap Analysis |
| Phase 2 | Planning & Documentation |
| Phase 3 | Process Implementation |
| Phase 4 | Training & Operationalization |
| Phase 5 | Evidence & Performance Monitoring |
| Phase 6 | Internal Audit |
| Phase 7 | Management Review |
| Phase 8 | Certification Readiness |
| Phase 9 | Certification Audit |
For an organization with reasonably mature ITSM processes, implementation can be significantly faster than for an organization starting from scratch.
Do not promise certification within an arbitrary number of days simply to win a project.
37. ISO 20000 Certification Cost in India
There is no single fixed ISO 20000 certification price.
The overall cost can include:
1. Consulting Cost
Depending on whether the organization requires:
- gap analysis;
- documentation;
- implementation;
- training;
- internal audit;
- certification preparation.
2. Certification Body Fees
These depend on factors such as:
- organization size;
- audit scope;
- service complexity;
- number of locations;
- audit duration;
- certification-body arrangements.
3. Internal Resources
Organizations should also account for:
- employee time;
- process-owner involvement;
- training;
- ITSM tool configuration;
- evidence generation.
4. Technology
There may be costs for:
- ITSM platforms;
- monitoring;
- CMDB;
- reporting;
- automation;
- knowledge management.
5. Travel / Site Requirements
Where applicable, additional costs may arise from multi-location or onsite audit arrangements.
38. How to Reduce ISO 20000 Implementation Cost
Cost optimization should not mean reducing the effectiveness of the SMS.
Instead:
Use Existing Processes
If incident management already works, improve it rather than rebuilding it.
Integrate With Existing ISO Systems
Organizations with ISO 9001 or ISO/IEC 27001 can potentially integrate common management-system activities.
Use Existing ITSM Tools
Do not purchase a new platform simply because the organization is pursuing certification.
Focus on Risk
Prioritize critical services and processes.
Avoid Documentation Overload
Create useful documented information rather than unnecessary paperwork.
Train Process Owners
Ownership should remain inside the organization rather than becoming completely consultant-dependent.
39. ISO 20000 + ISO 9001 + ISO/IEC 27001 Integrated Management System
For many technology organizations, an integrated approach can be attractive.
ISO 9001
Quality Management
ISO/IEC 20000-1
Service Management
ISO/IEC 27001
Information Security Management
Shared elements can include:
- context;
- leadership;
- objectives;
- documented information;
- competence;
- internal audit;
- management review;
- corrective action;
- continual improvement.
But integration must be carefully designed.
One document should not automatically be assumed to satisfy every requirement of three different standards.
40. ISO 20000 for SaaS Companies
SaaS companies are strong candidates for an ISO 20000 implementation because their business model revolves around delivering services.
Typical services may include:
- application hosting;
- cloud infrastructure;
- technical support;
- API services;
- managed platforms;
- customer onboarding;
- application maintenance.
The SMS can provide structure around:
Customer → Service → SLA → Delivery → Support → Measurement → Improvement
41. ISO 20000 for Managed Service Providers
For MSPs, service management is directly connected to the business model.
An MSP may need to manage:
- multiple customers;
- multiple SLAs;
- different support tiers;
- third-party suppliers;
- remote infrastructure;
- service desk;
- monitoring;
- incidents;
- changes;
- customer reporting.
ISO/IEC 20000-1 can provide a structured framework for demonstrating service management capability.
42. ISO 20000 for GCCs and Internal IT Departments
ISO 20000 is not limited to organizations selling IT services externally.
An internal IT organization can also have:
- internal customers;
- service catalogues;
- SLAs;
- service requests;
- incidents;
- infrastructure;
- suppliers;
- availability requirements;
- continuity requirements.
The organization should define an appropriate scope that reflects the actual services and organizational boundaries.
43. ISO 20000 and DevOps
ISO/IEC 20000-1 does not require an organization to abandon modern development and delivery approaches.
ISO’s practical guidance notes that ISO/IEC 20000 can fit with approaches such as Lean, Agile and DevOps.
The key is to ensure that speed does not eliminate appropriate service-management controls.
For example:
DevOps
→ Rapid deployment
ISO 20000
→ Controlled service transition
These do not have to be opposing concepts.
A mature organization can design controls that support rapid delivery while managing service risks.
44. Common ISO 20000 Certification Mistakes
Mistake 1 — Choosing the Scope Too Quickly
Scope should be based on actual service delivery.
Mistake 2 — Starting With Documentation
Start with understanding the services and processes.
Mistake 3 — Buying an ITSM Tool First
Technology should support the process.
Mistake 4 — Ignoring Customer Requirements
The SMS exists to support service requirements and value.
Mistake 5 — No Process Ownership
Every major process needs accountable ownership.
Mistake 6 — Weak Evidence
A procedure without operational records provides limited assurance.
Mistake 7 — No Meaningful KPIs
Measurement should support decisions.
Mistake 8 — Treating Internal Audit as a Final Formality
Internal audit should be a genuine readiness check.
Mistake 9 — Skipping Management Review
Management involvement is essential.
Mistake 10 — Assuming Certification Means Permanent Compliance
The SMS needs ongoing operation and improvement.
45. ISO/IEC 20000-1 Certification Readiness Checklist
Before approaching certification, review the following.
SMS Foundation
- Scope defined
- Interested parties identified
- Service requirements identified
- Service management policy established
- Objectives established
- Service Management Plan established
- Roles and responsibilities defined
Service Management
- Service portfolio established
- Service catalogue established
- SLA management implemented
- Relationship management implemented
- Supplier management implemented
- Demand management implemented
- Capacity management implemented
- Availability management implemented
- Service continuity implemented
- Information security management addressed
Operational Processes
- Incident management
- Service request management
- Problem management
- Change management
- Release/deployment management
- Configuration management
- Service reporting
Evaluation
- KPIs defined
- Measurements collected
- Service reports available
- Internal audit completed
- Management review completed
Improvement
- Nonconformities recorded
- Corrective actions implemented
- Effectiveness reviewed
- Continual improvement demonstrated
46. The Practical ISO 20000 Implementation Roadmap
A simple implementation roadmap can be visualized as:
STEP 1 — Understand
Business → Customers → Services → Requirements
STEP 2 — Define
Scope → Policy → Objectives → Responsibilities
STEP 3 — Plan
Risk → Service Management Plan → Resources
STEP 4 — Design
Processes → Procedures → Metrics → Tools
STEP 5 — Implement
Training → Process Deployment → Operations
STEP 6 — Measure
KPIs → SLA → Service Reports → Trends
STEP 7 — Audit
Internal Audit → Findings → Corrective Action
STEP 8 — Review
Management Review → Decisions → Improvement
STEP 9 — Certify
Certification Audit → Findings → Certification Decision
STEP 10 — Improve
Surveillance → Performance → Continual Improvement
47. What Makes an ISO 20000 Implementation Successful?
A successful implementation usually has five characteristics.
1. Management Ownership
Management understands that service management is a business capability.
2. Clear Service Scope
The organization knows exactly what it is managing.
3. Process Ownership
People are accountable for process performance.
4. Evidence-Based Management
Decisions are supported by service data.
5. Continual Improvement
The organization uses operational experience to improve.
Consultant’s Insight
At CK Associates, our practical approach to ISO management-system implementation is based on a simple principle:
Don’t implement ISO 20000 to create documents; implement it to create a controlled, measurable and continuously improving service-management system.
For an IT organization, the real value appears when:
Customer Requirement
↓
Service Requirement
↓
Service Design
↓
Controlled Delivery
↓
Incident / Request / Problem Management
↓
Measurement
↓
Management Review
↓
Corrective Action
↓
Continual Improvement
That is when ISO/IEC 20000-1 becomes more than a certification exercise.
It becomes part of the organization’s operating model.
ISO/IEC 20000-1:2018 — Key Takeaways
1. Start with the scope
Do not start with templates.
2. Conduct a genuine gap analysis
Understand the difference between current practice and ISO requirements.
3. Build the SMS around actual services
Do not create theoretical processes disconnected from operations.
4. Clause 6.3 matters
The Service Management Plan is an important part of the implementation architecture.
5. Clause 8 is operationally critical
The service management processes must work in practice.
6. Evidence is essential
The organization should be able to demonstrate what it actually does.
7. Internal audit comes before certification
Use it to identify weaknesses.
8. Management review is essential
Top management must evaluate performance and improvement.
9. Certification is an independent assessment
The certification body assesses conformity; ISO itself does not issue the certificate.
10. Continual improvement continues after certification
The certificate is not the finish line.
Final Conclusion
ISO/IEC 20000-1:2018 provides organizations with a structured framework for managing services from planning and design through transition, delivery, measurement and continual improvement. ISO describes the standard as a requirements-based SMS standard that can be used to demonstrate service-management capability and support conformity assessment.
A successful implementation therefore requires more than preparing procedures.
It requires the organization to understand its services, define requirements, establish responsibilities, implement appropriate processes, measure performance, maintain evidence, audit itself and continuously improve.
For a SaaS company, MSP, cloud provider, GCC or internal IT organization, the real objective should be:
Reliable services + controlled processes + measurable performance + customer confidence + continual improvement.
That is the real business value behind ISO/IEC 20000-1.
Why Trust This Guidance?
CK Associates — ISO Certification Consultancy
20+ Years Experience | 450+ Certification Projects | 8+ Consultants | Multi-Standard Expertise
Our consulting approach focuses on practical implementation rather than documentation alone, helping organizations translate ISO requirements into processes that can actually be operated, measured and audited.
Relevant ISO Experience
- 400+ ISO 9001 projects
- 25+ ISO/IEC 27001 projects
- 4+ ISO 42001 projects
- 45+ ISO 14001 projects
- 45+ ISO 45001 projects
About the Author
Sirish K
Founder & Lead ISO Consultant — CK Associates
Sirish K has 20+ years of experience in ISO consulting, management-system implementation, training, internal audits and certification readiness across multiple standards and industries.
His practical consulting philosophy is:
Understand the requirement → design the system → implement it → generate evidence → audit it → improve it.
Frequently Asked Questions
1. How long does ISO/IEC 20000-1 implementation take?
There is no universal implementation period. It depends on the organization’s size, scope, number of services, locations, existing ITSM maturity, documentation, technology and resource availability. A mature ITSM organization may require substantially less implementation work than an organization building formal service management processes for the first time.
2. Is ISO 20000-1 certification mandatory?
ISO/IEC 20000-1 certification is generally a voluntary conformity assessment unless a specific customer, contract, regulatory or other requirement makes it necessary for the organization.
3. Who provides ISO 20000 certification?
Certification is performed by an independent certification body rather than ISO itself.
4. Can a SaaS company get ISO 20000 certification?
Yes. SaaS organizations can define an appropriate SMS scope around the services they provide and implement the applicable ISO/IEC 20000-1 requirements.
5. Can an internal IT department get ISO 20000 certification?
Yes. The standard can be applied to an organizational unit or service environment where an appropriate scope can be established.
6. Do we need an ITSM tool for ISO 20000?
Not necessarily. Technology can support the SMS, but certification is based on conformity with the applicable requirements and effective implementation, not ownership of a particular ITSM software product.
7. Is ITIL certification the same as ISO 20000 certification?
No. ITIL and ISO/IEC 20000-1 serve different purposes. ITIL provides service-management practices and guidance, while ISO/IEC 20000-1 specifies requirements for a Service Management System and can support conformity assessment.
8. Can ISO 20000 be integrated with ISO 27001?
Yes. Organizations can integrate common management-system elements while addressing the distinct requirements and objectives of each standard.
9. What is the most important part of ISO 20000 implementation?
There is no single clause that replaces the others. However, effective implementation requires the organization to connect the management-system foundation in Clauses 4–7 with operational service management in Clause 8, performance evaluation in Clause 9 and improvement in Clause 10.
10. Is ISO/IEC 20000-1:2018 still current?
Yes. ISO currently lists ISO/IEC 20000-1:2018 as the current published edition; ISO also lists Amendment 1:2024, which applies climate-action changes to the 2018 standard.